https://goxterm.interloop.live:8443 for remote infrastructure management.
The Modern Web-Based Terminal
& Remote Infrastructure Gateway
GoXterm bridges the gap between traditional desktop terminal emulators and heavy enterprise bastions. Access SSH, Telnet, Local Shell, SFTP files, and HTML5 Remote Desktop from any browser — protected by hardware-free bot defense, multi-factor authentication, and containerized access control.
Built for Daily Remote Productivity
Experience a full-featured, zero-install desktop environment inside your web browser. Seamlessly manage Linux servers, network switches, and Windows hosts.
[GoXterm Gateway Engine v2.0-RELEASE • Build 20260920.248]
# System health & network multiplexing report
Status: ONLINE (Zero-CGO Pure-Go Runtime)
Bound Endpoint: https://0.0.0.0:8443 (TLS & Encrypted RBAC Gateway)
Ingress Access: Loopback Desktop Auto-Login + Remote Web Browser
Authentication: LDAP / Active Directory + 2FA Active (TOTP/SMS/Email)
Bot Defense: Cryptographic PoW Gatekeeper ENABLED
Active Remote Sessions: 4 (SSH: 2, Telnet: 1, VNC HTML5: 1)
rliu@prod-bastion:~$ docker ps --format "table {{.Names}}\t{{.Status}}\t{{.Ports}}"
NAMES STATUS PORTS
api-gateway-live Up 14 days (healthy) 0.0.0.0:8080->8080/tcp
postgres-db-core Up 28 days 127.0.0.1:5432->5432/tcp
redis-cache-tier Up 28 days 127.0.0.1:6379->6379/tcp
Global Collaboration via Secure Bastion Enclave
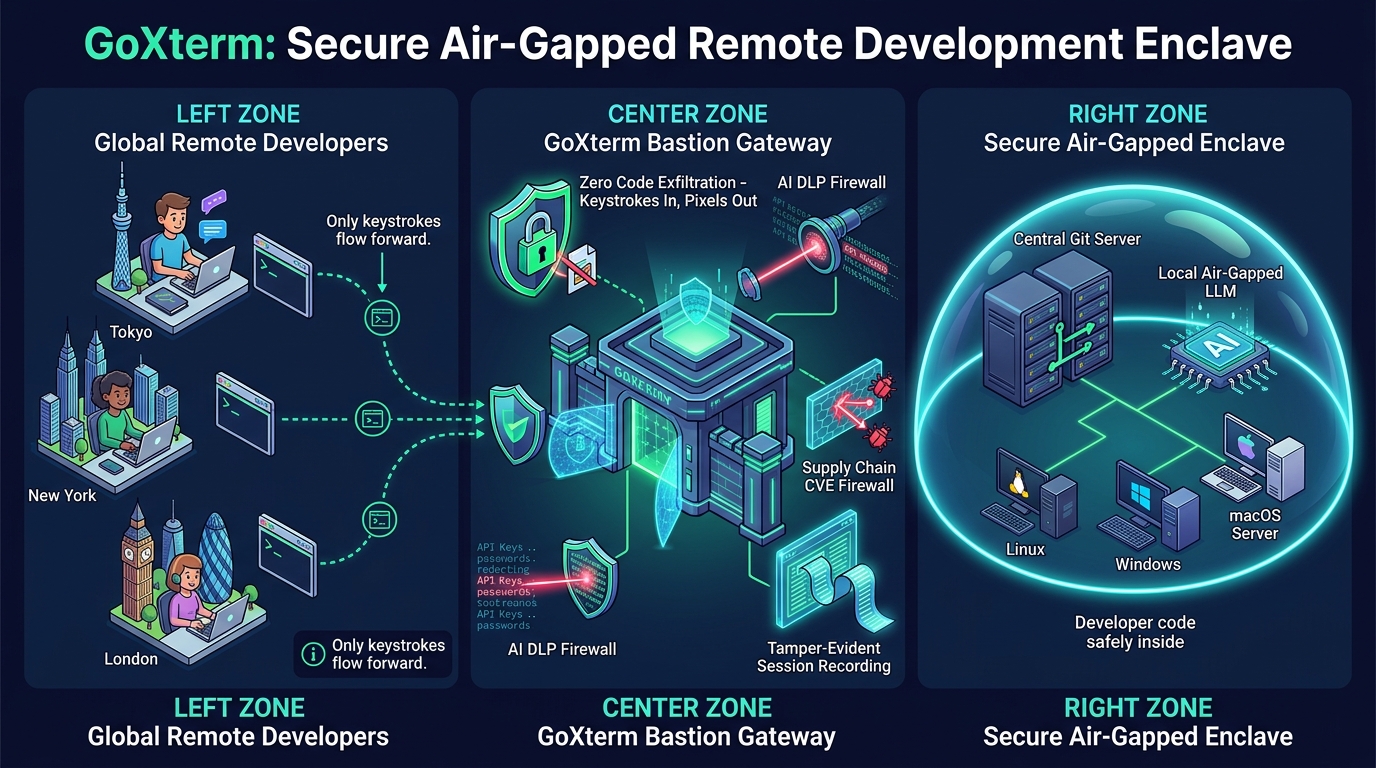
Built for Demanding Infrastructure
Everything needed for secure daily operations, zero-maintenance bastions, and enterprise access control.
Multi-Protocol Web Terminal
High-performance xterm.js terminal with pure-Go WebSocket bridge. Includes native SSH, pure-Go RFC 854 Telnet for legacy switches/routers, and integrated local shell console.
SSH • Telnet • Local ShellRemote Desktop (VNC & RDP)
Directly access remote GUI environments. Enjoy zero-install in-browser HTML5 VNC (via embedded noVNC) plus native 60 FPS RDP integration with dynamic .rdp profile generation, 1-click Windows launch, and zero-trust gateway tunneling.
HTML5 VNC • Native RDP LauncherSession Containers & RBAC
Organize sessions into containers with fine-grained permission scopes: Private (creator only), Group (authorized team groups), and Public. Move sessions with one click.
Container Permissions • User GroupsLDAP & Active Directory
Pure-Go LDAP/AD client supporting LDAPS (Port 636) and StartTLS. Authenticate corporate domain credentials, extract group memberships, and auto-provision admin or operator roles.
LDAPS • StartTLS • AD IntegrationTriple-Tier 2FA Security
Secure every user with Multi-Factor Authentication: offline TOTP (Google/Microsoft Authenticator), Email OTP via outbound SMTP alerts, or SMS OTP to mobile phones. Includes air-gapped emergency disaster recovery.
TOTP • Email OTP • SMS OTPBot-Defense Gatekeeper
Client-side cryptographic Proof-of-Work (PoW) verification stops automated brute-force attacks and password sprayers in their tracks without requiring privacy-invasive Google reCAPTCHA.
Proof-of-Work • Anti-Brute-ForceDual-Pane SFTP Studio & Recursive Folder Transfer
Integrated left sidebar SFTP browser for active sessions. Browse remote file hierarchies, upload entire nested project folders recursively (via folder picker or drag-and-drop), download remote directories on the fly as streaming .zip archives, and edit configuration files in-place.
Remote Tech Support
Assist remote customers or team members without third-party tools. Generate 6-digit session PINs, share real-time screens, and chat interactively over an end-to-end WebSocket channel.
Enterprise Bastion • Screen Sharing • Live AssistanceInstant Desktop Auto-Login
Combines the zero-friction experience of a native desktop terminal with the security of an enterprise gateway. Launches seamlessly on loopback with ephemeral single-use auto-login.
Zero-Friction Launch • Single-User FreeAES-256 Secret Vault & Workload API
Built-in zero-cloud credential and note vault. Protect root passphrases, API tokens, and TLS private keys with native AES-256-GCM encryption at rest. Features headless machine accounts (api_user), passwordless OIDC identity, and programmatic reveal endpoints.
AI Proxy Gateway & DLP Firewall
Enterprise OpenAI-compatible proxy (/v1) routing prompts to OpenAI, Anthropic, DeepSeek, or air-gapped local Ollama. Sub-millisecond pure-Go regex DLP intercepts and masks/blocks secrets, API keys, credentials, and internal IP leaks.
Dependency Proxy & CVE Firewall
Multi-ecosystem caching proxy for Python (PyPI), Node.js (NPM), Go Modules, and Debian/Ubuntu (APT). Integrates real-time OSV.dev CVE intelligence to drop High/Critical supply chain vulnerabilities before they reach dev enclaves.
Smartphone-Adaptive Mobile Workspace
Full-featured on-call terminal access from any smartphone or tablet. Off-canvas navigation drawer, dynamic visual viewport (100dvh) that auto-resizes around soft keyboards, single-tap session launching, bottom-sheet modals, and a pinned quick-key accessory ribbon.
Air-Gapped Break-Glass Protection
Guarantees emergency recovery superuser privileges cannot be exploited remotely. Strictly disabled by default, it requires physical server-side activation with configurable TTL expiry and instant single-use self-destruction upon login.
Single-Use Self-Destruction • Air-Gapped Trigger • Root DefenseIn-Browser SFTP Editor & Diff Engine
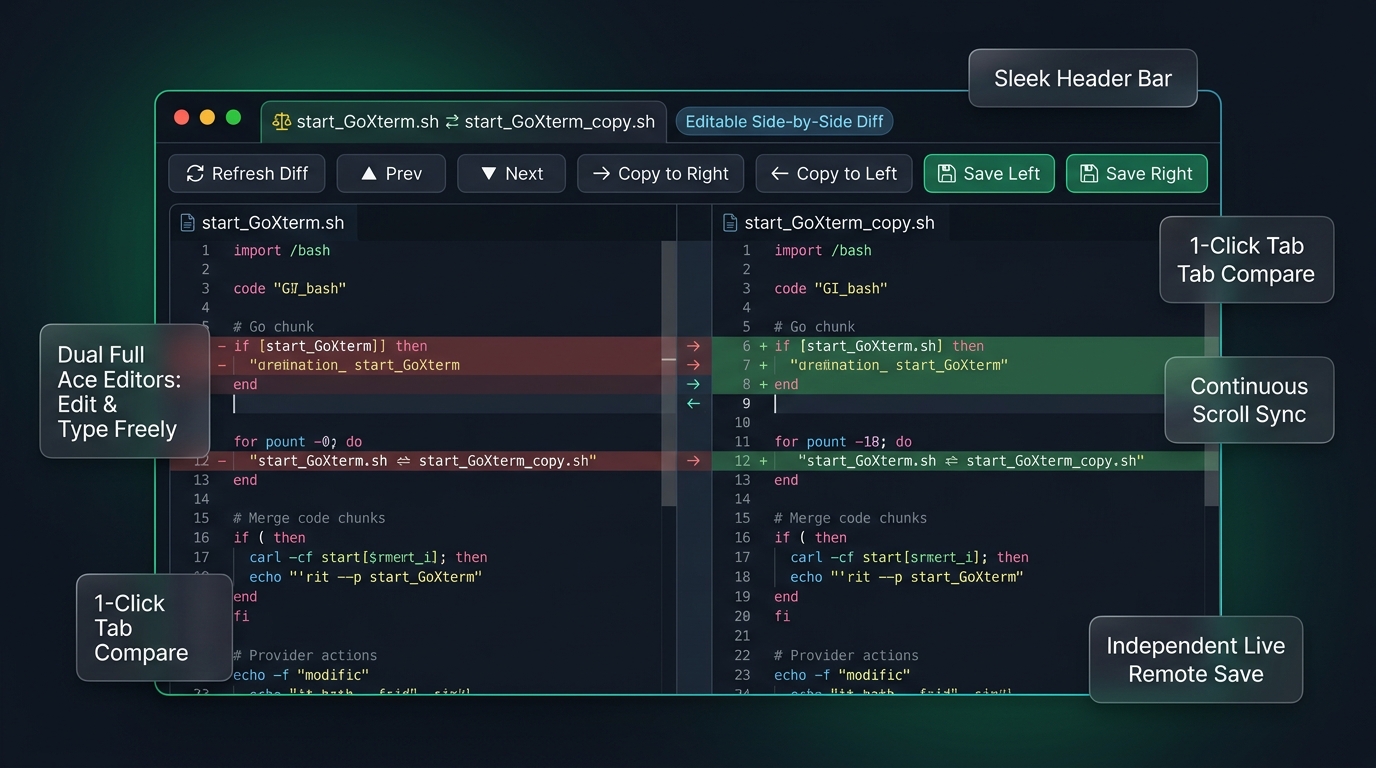
Live GUI text editor for remote scripts, configs, and logs directly from SSH sessions with syntax highlighting (JSON, YAML, Bash, INI, Python, Markdown). Includes Editable Side-by-Side Diff with 1-click tab comparison (⚖️ Compare), continuous scroll sync, hunk merge buttons (➔ / ←), and independent remote saving (Ctrl+S).
Dual-Ace Editor • 1-Click Tab Compare • Synchronized PanesClickable File Links & Stack Jumps
Turns the command-line into a first-class interactive GUI. Hover over any file path in ls, git status, or compiler stack traces (e.g. main.go:42:15) and click to launch the file directly in the in-browser Remote Ace Editor jumped to that exact line and column—completely bypassing manual SFTP tree browsing!
Top 100 Command Quick Reference
Privacy-conscious terminal command tracker aggregating your top 100 most frequent shell commands. Accessible from anywhere via Ctrl+Shift+H for instant search, 1-click execution (⚡ Run), pasting into the terminal buffer (📋 Paste), and starring mission-critical one-liners.
Usage Analytics • 1-Click Run • Pinned Production One-LinersActive-Standby HA & Keepalived VIP
Enterprise high availability without the complexity of external clusters. Single-node standalone by default (<40MB RAM) with Day-2 clustering enabled via the Admin UI. Uses standard Keepalived Virtual IP (VIP) ingress routing, cryptographic join tokens, and an odd-numbered 3-node VRRP quorum architecture (priorities 102/101/100) for deterministic split-brain prevention without standalone witness daemons. Includes live WAL replication sync, graceful switchover, and disaster recovery force promotion.
Enterprise Clustering • Keepalived VIP • 3-Node QuorumSecret Vault & Machine Identity (api_user)
Centralized Zero-Trust secrets management built directly into GoXterm with zero external daemon dependencies. Securely escrow API keys, database credentials, TLS certificates, and tokens with AES-256-GCM authenticated column encryption. Features dedicated headless machine accounts (api_user) strictly blocked from GUI login, scoped Bearer tokens with usage/TTL bounds, and trusted_hosts network CIDR allowlisting for CI/CD runners and microservices.
Air-Gapped Enclave: Configurable One-Way Traffic Controls
Security and developer convenience, balanced on your terms. Administrators can dynamically tune isolation levels per organization policy: enjoy full bidirectional convenience (fluid SFTP file transfers and copy & paste) in standard environments, or effortlessly lock down to One-Way Inbound Enclave mode (blocking SFTP downloads and restricting clipboard to paste-only) when air-gapped intellectual property defense demands that "No code leaves the enclave".
Cross-Border & Hotel Wi-Fi WAN Acceleration
Field-tested across trans-Pacific hotel links (working from a hotel in China connected back to a remote Ubuntu workstation). Instant server-side Gatekeeper PoW rendering (0ms first paint), background script deferral, 80% HTTP gzip payload compression, and macOS trackpad back-swipe protection make intercontinental remote development feel indistinguishable from sitting at home on a local LAN.
“Dev on the Go” Mobile & In-Car Coding Studio
Built for shipping code from anywhere—even from a phone while riding in a car. Features a 1-tap TMUX session create/attach button for bulletproof cellular persistence, 1-tap 📜 COPY scrollback toggle with kinetic touch-fling scrolling, a strict on-demand ⌨️ keyboard lock that never pops up uninvited on quick-key taps, and an LCP autocomplete sync engine that prevents mobile predictive keyboards from duplicating words or refreshing the terminal.
Operational Best Practices & Security Guide
Practical rules and workflows to maximize efficiency, protect credentials, and maintain Zero-Trust isolation across all your devices.
How you access GoXterm should depend on whether your client machine is a trusted personal workstation or an untrusted public computer.
-
Install GoXterm Extension: Download the Web Bastion extension (.zip) and load unpacked into Chrome/Edge for instant 1-click isolated routing without modifying system settings.
-
Selective Split-Tunneling: Only requests targeting authorized internal subnets (e.g.
10.x.x.x,192.168.x.x) route through GoXterm. All other internet traffic (Google, SaaS, intranet) remains 100% direct with zero latency. -
1-Click Launcher Scripts: Alternatively, use the generated
.bat(Windows) or.command(macOS) script to spawn an isolated browser profile configured exclusively for your active session. -
Save Bookmarks in Vault: Keep server bookmarks organized into hierarchical folders. All host credentials, private keys, and passphrases are encrypted at rest with AES-256-GCM.
-
NEVER Install Browser Extensions or Scripts: Do NOT download the extension or save
.bat/.commandscripts on public PCs. Unpacked files and proxy settings persist in local folders and can be recovered by subsequent users! -
Use Zero-Footprint Web Canvas: Rely exclusively on GoXterm's native in-browser terminal emulator, SFTP side-drawer, or in-browser HTML5 VNC viewer. They render entirely inside ephemeral browser canvas memory with zero files written to disk.
-
Always Use Incognito / InPrivate: Open GoXterm only inside an Incognito window so cookies, history, and cached pages are destroyed as soon as the window closes.
-
Always Explicitly Click "Logout": Never merely close the browser tab. Clicking Logout immediately destroys your session token and revokes all backend proxy authorizations on the server.
Adopt these best practices during day-to-day operations to keep your infrastructure resilient against unauthorized access.
-
Enable Multi-Factor Authentication (TOTP): Pair your account with Google Authenticator, 1Password, or YubiKey. Requiring 2FA blocks 99% of automated credential stuffing attacks.
-
Never Store Passwords in Plaintext Notes: Use GoXterm's built-in credential vault. Passwords and private keys are encrypted with authenticated AES-256-GCM before touching SQLite.
-
Protect the Vault Passphrase: Set a strong master passphrase for your server vault. Even if raw database backups are compromised, encrypted fields remain indecipherable.
-
1-Click Password Rotation: When editing SSH, RDP, or remote hosts, click Rotate Password to cryptographically generate a high-entropy 20-character password (NIST SP 800-63B compliant) with automatic clipboard copy.
-
Audit Active Sessions: Check Settings > Active Sessions periodically to view device types, client IPs, and login timestamps connected to your identity.
-
One-Click "Revoke Other Sessions": Instantly terminate stale logins from old phones, tablets, or borrowed laptops with a single click.
-
Configure Idle Lockout: Enforce an automatic 15-30 minute session idle timeout to lock unattended browser tabs on your office desk or home workstation.
-
1-Click Enclave Access: Open internal admin consoles (ESXi, Proxmox, iDRAC, routers, Grafana) directly in Chrome tabs with zero system-wide network disruption.
-
Just-In-Time (JIT) 2-Hour TTL: Target appliance routes are granted dynamically upon session launch and expire automatically after 2 hours.
-
Automated SSRF Defense: GoXterm's forward proxy automatically drops requests targeting cloud metadata endpoints (
169.254.169.254) or loopback interfaces.
-
Integrated SFTP Drawer: Open the side-drawer on active SSH tabs to drag-and-drop upload/download files, edit configs in-browser, or chmod permissions without external tools.
-
Containerized Organization: Group servers into shared team containers (e.g.
Production/,Staging/) with granular RBAC permissions. -
Audit Logs & Recordings: Review automated session recordings and audit logs for compliance, troubleshooting, and post-incident investigation.
-
Disabled by Default: Emergency break-glass superuser access is strictly disabled during normal operation to prevent internet-facing brute-force or credential stuffing.
-
Host-Level Physical Authorization: Activating emergency recovery requires direct server host access with time-limited TTL expiry. Detailed CLI commands and operational runbooks are documented in the Administrator Guide.
-
Single-Use Self-Destruction: The moment emergency recovery successfully authenticates, the trigger is automatically consumed and destroyed, instantly locking the door behind the administrator.
-
Off-Canvas Drawer & 1-Tap Connect: On mobile screens (≤ 768px), tap the hamburger menu to view sessions; single-tapping any host immediately launches full-screen terminal and closes the drawer.
-
Virtual Accessory Key Ribbon: Dedicated bottom-pinned touch ribbon provides
ESC,TAB,^C(kill process), stickyCTRLtoggle, navigation arrows,|,/,-,~, and soft keyboard focus. -
Visual Viewport Auto-Fit (100dvh): Listens to mobile virtual keyboard popups via
window.visualViewportand automatically resizes terminal rows and columns so terminal output is never obscured.
Maximize daily engineering velocity with built-in zero-friction editing, visual diffing, and intelligent command history reference.
-
Frictionless In-Place Editing: In any active SSH session, open the SFTP drawer, click
•••→ Edit (or double-click) to open scripts, YAML configs, and server logs directly in the browser. -
Syntax Highlighting: Automatically formats JSON, YAML, Bash scripts, INI/systemd units, Python, and Markdown with real-time gutter line numbering and cursor metrics.
-
Integrated Find & Replace: Press Ctrl+F (or Ctrl+H) to search text with match counters, case-sensitivity toggles (
Aa), whole-word boundaries (\b), regex support (.*), and one-click Replace All. -
Side-by-Side In-Editor Diff: Click ⚖️ Diff in the editor header to instantly compare original remote content against your unsaved local buffer with synchronized scrolling and addition/deletion line highlights.
-
Instant Server Sync: Press Ctrl+S (Cmd+S) to save and stream updates straight to the remote host without local downloading or file staging.
-
Editable Dual-Ace Side-by-Side Diff: Open two files into editor tabs, then click ⚖️ Compare on the active tab to compare against the left tab. Edit directly in either pane, port code hunks with 1-click merge buttons (➔ / ←), synchronize scrolling, and save directly to the remote host with Ctrl+S.
-
Global Quick Reference (Ctrl+Shift+H): Press Ctrl+Shift+H or click 📜 Commands on the topbar to open the Top 100 command reference modal from any screen.
-
Run, Paste & Pin Actions: Click ⚡ Run to execute immediately with Enter, 📋 Paste to insert into the terminal without Enter for argument editing, or ⭐ Pin to lock vital one-liners to the top.
-
Privacy-Preserving History: Commands are stored purely in client-side
localStoragewith sensitive token/credential filters, keeping your credentials off the server.
-
Zero-Client Browser Canvas: Connect directly to Linux GUI environments (GNOME, XFCE, KDE) or Raspberry Pi desktops inside your browser tab without installing third-party viewer software.
-
Pure-Go WebSocket Bridge: High-throughput RFB streaming multiplexed through GoXterm's
/ws/vncendpoint with zero CGO dependencies. -
Integrated Desktop Controls: Access dedicated toolbar controls for Send Ctrl+Alt+Del, clipboard synchronization, full-screen canvas expansion, and remote scaling modes.
-
Direct Mode (Community): 1-click launch via Windows
mstsc.exeor download pre-configured.rdpprofiles with saved credentials, screen resolution, and audio redirection. -
Zero-Trust Tunneling (Gateway Pro): Issue ephemeral one-time tickets and launch
goxterm-tunnelto proxy native Microsoft Remote Desktop through GoXterm's WebSocket gateway (/ws/rdp) without exposing raw port 3389 or running a VPN. -
Uncompromised Performance: Avoid sluggish in-browser JavaScript RDP rendering; enjoy full 60 FPS RemoteFX/AV1 hardware acceleration and native multi-monitor support.
api_user)
-
Headless Machine Accounts: Create dedicated
api_useraccounts for CI/CD runners, pipelines, and microservices. The gateway strictly denies interactive web GUI logins (403 Forbidden) for machine accounts. -
Granular Folder & Secret Scopes: Grant read/write permissions at the container folder or individual secret level. Automated workloads only access secrets within their assigned scope.
-
Zero-Trust Network Allowlisting: Bind vault sessions to CIDR subnets using
trusted_hosts(e.g.10.240.0.0/16, 192.168.1.50/32). Secret reveal requests originating outside allowed IPs are instantly rejected with 403 Forbidden. -
Self-Destructing & Expiring Tokens: Configure Bearer tokens with strict expiration TTLs, single-use counters (
max_uses=1) for bootstrap automation, or client-side IP subnet locks.
-
Secure Note Distribution Pattern: Administrators store issued
api_userBearer tokens in an encrypted Note session and grant read-only folder access to specific operator groups (e.g.DevOps,SRE) without emailing plaintext tokens. -
AES-256-GCM Column Encryption: All vault payloads, secrets, and private tokens are encrypted with authenticated AES-256-GCM before writing to the database, ensuring zero plaintext exposure in logs or backups.
-
1-Click Secret Reveal & Copy: Authorized operators can view masked secrets (
••••••••), trigger a temporary reveal, or copy the payload straight to the clipboard with full audit logging. -
Immediate Token Revocation & Rotation: Rotate or revoke tokens instantly from the Admin Users modal, immediately terminating all active API sessions without restarting the server.
AI Proxy & Dependency Firewall Setup
Quickly configure developer toolchains, AI assistants, and security policies with zero infrastructure friction.
🤖 AI Proxy Gateway & DLP Firewall
GoXterm exposes an OpenAI-compatible /v1/chat/completions endpoint. Point any AI coding tool, IDE extension, or Python/Node SDK to GoXterm to enforce real-time DLP inspection before prompts leave your enclave.
$ ./scripts/build.sh ai # or: go build -tags aiproxy -o goxterm .
# Launch gateway with upstream provider key:
$ OPENAI_API_KEY="sk-..." ./goxterm -mode gateway
$ export OPENAI_BASE_URL="https://goxterm.internal:8443/v1"
$ export OPENAI_API_KEY="your-goxterm-jwt-token"
# Or in Cursor / Continue config.json:
{ "apiBase": "https://goxterm.internal:8443/v1", "model": "gpt-4o" }
Configure custom DLP regex rules, redaction actions (mask or block), and compliance exemptions directly via the GoXterm Web Console or authenticated Admin APIs.
🛡️ View DLP Admin API Specification in Admin Guide →📦 Dependency Proxy & Supply Chain Firewall
Enclave build environments download packages from GoXterm's caching endpoints. Any library exhibiting High or Critical CVE vulnerabilities is rejected in real time with HTTP 403 Forbidden.
$ ./scripts/build.sh pkg && ./goxterm
# Option B: Run dedicated micro-daemon (25 MB RAM):
$ ./goxterm-pkg -listen :8081 -upstream-npm https://registry.npmjs.org -cve-block=true
$ pip install --index-url https://goxterm.internal:8443/pypi/simple/ flask
# 🟩 Node.js (NPM): ~/.npmrc or CLI
$ npm config set registry https://goxterm.internal:8443/npm/
# 🔷 Go Modules: environment variable
$ export GOPROXY="https://goxterm.internal:8443/go,direct"
# 🐧 Debian / Ubuntu: /etc/apt/sources.list.d/goxterm.list
$ deb https://goxterm.internal:8443/apt/debian bookworm main
Inspect blocked vulnerability events, review package caches, and test new ecosystem libraries via the Admin Console or internal security APIs.
🛡️ View Supply Chain Admin API in Admin Guide →🛡️ Active-Standby HA & Keepalived VIP
GoXterm features zero-friction Day-2 clustering. Start with a lightweight single-node instance (<40MB RAM) and scale seamlessly into a high-availability active-standby cluster directly through the Admin UI.
Open 🛡️ High Availability in the Admin UI, specify your Virtual IP (e.g. 192.168.1.100), interface (eth0), and assign Priority 102. Click Generate Join Token.
On secondary nodes, paste the cryptographically signed Join Token into the Join Existing Cluster wizard. Assign Priority 101 to Node 2 and Priority 100 to Node 3 to establish an odd-numbered VRRP quorum that prevents split-brain.
Download tailored keepalived.conf configurations directly from the Admin Dashboard for Nodes 1, 2, and 3. Keepalived probes /api/ha/health every 2 seconds, maintaining VIP ownership on the active primary and switching over automatically in <1 second.
Built for Hostile Public Perimeters
GoXterm was architected from day one to be safely exposed directly to the public internet.
ENC:v1:...). A decoupled 256-bit vault key ensures sensitive secrets remain unreadable even if raw SQLite databases are inspected.Hacker Attack Vectors & Layered Defensive Countermeasures
A rigorous threat model detailing how an adversary attempts to breach the perimeter, APIs, or data stores, and the cryptographic, network, and identity controls neutralizing each vector.
| Attack Vector & Target | Adversary Strategy & Objective | GoXterm Defensive Countermeasure & Architectural Guard |
|---|---|---|
|
1. Credential Stuffing & Password Spray Gateway Perimeter |
Automated botnet spraying leaked credentials or dictionary combinations against /api/login to hijack administrator accounts. |
• Dual-Dimensional Rate Limiting: Enforces exponential IP lockouts (5 failures = 15m lockout, scaling to 24h jail) alongside per-username account freezes. • Proof-of-Work (PoW) Shield: Requires client browser to solve cryptographic SHA-256 challenge before submitting auth packets. • Mandatory 2FA / MFA: TOTP (RFC 6238), Email OTP, or SMS challenges block 99.9% of automated credential stuffing. |
|
2. Session Hijacking & Token Interception Client Web Portal |
Sniffing tokens over untrusted Wi-Fi, extracting session tokens from XSS payloads, or reusing stale cookies from public kiosks. |
• Zero Plaintext HTTP: Automatic TLS 1.3 with ACME / Let's Encrypt and strict HSTS headers. • Hardened Cookie Directives: Tokens marked HttpOnly, SameSite=Strict, and Secure.• Remote Invalidation: 1-click "Revoke Other Sessions" and automatic idle timeouts terminate session tokens on the server immediately. |
|
3. Leaked Machine Tokens (CI/CD / Git) API Identity |
An engineer accidentally commits an automated pipeline Bearer token (gox_sec_...) or API key to a public GitHub repository. |
• Zero-Trust Network Gating (trusted_hosts): Secret reveal requests originating outside authorized CIDR subnets (e.g. 10.240.0.0/16) are instantly rejected with 403 Forbidden.• Token Bounds: Enforces strict expiration TTLs, single-use counters ( max_uses=1), and client IP allowlists.• Headless api_user: Machine accounts are permanently blocked from web GUI logins (403 Forbidden).
|
|
4. Cold Database Exfiltration & Backup Theft Data at Rest |
An attacker exfiltrates raw SQLite database files (data/goxterm.db) via backup repository compromise or volume snapshot theft. |
• Decoupled Column AES-256-GCM: Host passwords, private keys, session notes, and vault secrets are encrypted with ENC:v1:... authenticated ciphertext.• Air-Gapped Key Decoupling: Master key ( data/.vault.key or GOXTERM_VAULT_KEY) is stored separately under strict 0600 permissions. Database files alone yield zero usable plaintext.
|
|
5. Broken Object Level Auth (BOLA / IDOR) Access Control |
Tampering with resource identifiers (e.g. GET /api/sessions/{other_id}) to inspect, reveal, or modify other teams' infrastructure secrets. |
• Cryptographic Scope Enforcement: All DB queries strictly join authenticated user_id and caller's RBAC group IDs.• Folder ACL Gating: Containers are enforced as private, group, or public. Cross-tenant tampering returns 403 Forbidden or 404 Not Found.
|
|
6. Server-Side Request Forgery (SSRF) Network Enclave |
Using the Web Bastion forward proxy to scan internal loopbacks (127.0.0.1) or cloud metadata services (169.254.169.254). |
• Automated Loopback & Metadata Drop: Integrated filter blocks all requests targeting loopback addresses, link-local metadata, or broadcast interfaces. • Just-In-Time (JIT) 2-Hour TTL: Target host access routes are granted dynamically upon session launch and expire automatically. |
|
7. Remote Shell & Command Injection Execution Path |
Injecting shell metacharacters (; rm -rf /; $(...)) into session names, parameters, or SFTP drawer file paths. |
• Native RFC 4254 SSH Channels: Direct binary SSH framing without shell command string wrapping (no sh -c execution).• Path Traversal Guards: SFTP and file download APIs resolve paths with filepath.Clean and strictly reject traversal (../).
|
|
8. Memory Corruption & Buffer Overflows Binary Integrity |
Exploiting heap overflows, use-after-free, or native library vulnerabilities (e.g. OpenSSL Heartbleed, Log4j). |
• 100% Pure Go (`CGO_ENABLED=0`): Type-safe, memory-managed compiled binary with runtime slice boundary checks and garbage collection. • Zero External Daemons: Single self-contained binary (<40MB) eliminating attack surfaces from Redis, external brokers, or unpatched C runtimes. |
|
9. AI Prompt Data Leakage (LLM DLP) Developer Enclave |
Engineers pasting proprietary API keys, database credentials, or customer PII into external AI completion prompts (Cursor, Continue). |
• Inline AI DLP Firewall: Integrated high-speed regex & Shannon entropy DLP engine (/v1/chat/completions) inspects outgoing prompts in real time and masks or blocks sensitive tokens before transmission.
|
|
10. Emergency Backdoor Exploitation Disaster Recovery |
Adversaries scanning the internet to probe emergency superuser recovery mechanisms (grand_admin). |
• Disabled by Default: Emergency break-glass access is dormant during normal operations. • Physical Host-Level Authorization: Activation requires direct server host CLI execution with time-limited TTL expiry. • Single-Use Self-Destruction: The trigger is atomically consumed and wiped upon login, locking the door behind the recovery session. |
|
11. Source Code & Secret Exfiltration Enclave Egress |
Remote developers or compromised contractor laptops copying intellectual property, git repositories, or sensitive data out of the development enclave. |
• One-Way Inbound Enclave Mode: Keystrokes in, pixels out. Code stays permanently anchored inside the enclave. • SFTP Exfiltration Lockout: Backend file download endpoint ( GET /api/sftp/download) returns 403 Forbidden when sftp_download_policy=disabled.• Inbound-Only Clipboard: Developers can paste code into the terminal, but copying out triggers an exfiltration block alert. • RDP Clipboard Suppression: Windows RDP profiles automatically force redirectclipboard:i:0.
|
|
12. Supply Chain Dependency Poisoning Inbound Ingress |
Build runners or developers pulling packages with known High/Critical CVEs or typosquatted malware from public registries (pip, npm, maven, apt). |
• Real-Time CVE Firewall: Multi-ecosystem caching proxy cross-references package versions against OSV.dev vulnerability intelligence. • Zero-Config Build Tool Integration: Drop-in mirror redirection via pip.conf, .npmrc, and settings.xml.
|
- Seamless loopback desktop auto-login
- Direct connection to local routers & Pis
- Zero cloud reliance • 100% offline
- Session bookmark import (.mxtsessions / JSON)
- Clientless access from iPad, Mac, or PC
- Encrypted HTTPS web access from browser or mobile
- Dynamic dev port forwarding previewer
- Zero VPN setup needed for web apps
- LDAP / Active Directory authentication
- Multi-user RBAC & user groups
- Private & group container permissions
- Embedded zero-maintenance SQLite DB
Transparent Licensing Built for Enterprise Infrastructure
Zero telemetry. Fully offline Ed25519 cryptographic validation. No hidden cloud phone-home.
- ✓ Single-User Admin License • Free Forever
- ✓ Zero-Friction Desktop Auto-Login via Loopback
- ✓ Unlimited local shells, SSH & pure-Go Telnet
- ✓ In-Browser SFTP File Editor & Side-by-Side Diff
- ✓ Dev Port Previewer (
/preview/...) & Web Proxy - ✓ In-browser HTML5 VNC viewer & native RDP profile launcher
- ✓ Top 100 Command Quick Reference (Ctrl+Shift+H)
- ✓ Web Serial client (USB / COM dongles)
- ✓ Encrypted SQLite Database & AES-256 Secret Vault
- ✓ Zero cloud connection, 100% private & offline
- ✓ Everything in Community Edition
- ✓ Automatic 30-Day Full Evaluation Trial included
- ✓ Multi-user centralized bastion & floating seats pool
- ✓ Ephemeral Zero-Trust RDP Native Client Tunneling
- ✓ Remote IT Helpdesk & Support Agent (reverse VNC)
- ✓ Session Containers with Private/Group RBAC scopes
- ✓ Corporate LDAP & Active Directory (LDAPS / StartTLS)
- ✓ Triple-Tier 2FA (TOTP, Email OTP & SMS)
- ✓ Cryptographic Proof-of-Work bot & brute-force defense
- ✓ Built-in TLS & automated certificate management
- ✓ Everything in Gateway Pro
- ✓ Centralized OIDC Workload Identity via API (K8s, CI/CD)
- ✓ Active-Standby High Availability (Keepalived VIP & Quorum)
- ✓ Smart Audit & SCRM (Keystroke vector search & VFR video)
- ✓ AI Proxy Gateway (
/v1) with inline regex DLP Firewall - ✓ Dependency Proxy & Supply Chain CVE Firewall (PyPI/NPM/Go/APT)
- ✓ Air-Gapped Break-Glass emergency disaster recovery
- ✓ 100% Air-gapped offline activation (zero telemetry)
- ✓ Custom seat pools, multi-node clustering & priority SLA
Customer Licensing & Activation Workflow
GoXterm licenses are signed with high-assurance Ed25519 asymmetric cryptography. The server verifies licenses purely using an embedded public key, guaranteeing zero outbound telemetry and 100% compliance in air-gapped enclaves.
Server Host ID (e.g. GOX-HOST-A1B2-C3D4).
GOXTERM-LIC-...) on your confirmation screen and delivers it via email.
Download Free & Open Source
Zero-dependency, standalone pre-compiled binaries. Extract and run with zero external prerequisites.
Windows (x86_64)
Windows 10, 11, Windows Server. Includes batch startup script & headless autostart service.
⬇ Download ZIP (x64)macOS (Apple Silicon)
M1, M2, M3, M4 Macs. Native arm64 architecture with zero Rosetta emulation needed.
⬇ Download ZIP (arm64)macOS (Intel x86_64)
Intel-based MacBooks, iMacs, and Mac Minis. Includes launchd daemon autostart scripts.
⬇ Download ZIP (x64)Linux (x86_64 / amd64)
Ubuntu, Debian, RHEL, CentOS, Rocky Linux, Arch. Includes systemd autostart support.
⬇ Download tar.gz (x64)Linux ARM64 / Pi
Raspberry Pi 4/5, AWS Graviton, Oracle ARM, embedded boards running 64-bit Linux.
⬇ Download tar.gz (arm64)GitHub Releases
Full source code, changelogs, checksums, and issue tracking hosted on GitHub.
🐙 View GitHub Releases⚡ Quick 3-Step Deployment:
- Extract the archive: Unzip or run
tar -xzf goxterm-*.tar.gzin your target directory. - Configure startup (Optional): Edit
start_GoXterm.sh(or.bat) to enable Gateway mode, set your initial admin password, or configure SMTP for dynamic IP tracking. - Launch: Run
./start_GoXterm.shand openhttps://localhost:8443in any browser!